Mastering AWS CLI: Commands for Cloud Engineering, DevOps, and AI Workloads
One identity check, aws sts get-caller-identity, before any command that can create a billable resource. AWS CLI 2.37.12 on 11 October 2026.
Tagged

One identity check, aws sts get-caller-identity, before any command that can create a billable resource. AWS CLI 2.37.12 on 11 October 2026.

As of 3 October 2026 the managed AWS MCP Server has endpoints in 8 Regions, a hard cap of 10 authenticated requests per second, and two auth paths. OAuth is the single-account start. SigV4 is the one that can hide write tools and switch accounts.

On September 29, 2026 AWS opened Bedrock Managed Agents, powered by OpenAI, in preview: 3 US Regions, no extra preview charge, and an 8-hour compute window in the AgentCore example. AWS runs the conversation. Your compute runs the tools.

On August 19, 2026 AWS enabled live-web fetch for Bedrock Web Search in 3 US Regions. Default external_web_access is true; AmazonBedrockFullAccess still does not grant ExternalWebAccess — and the 403 does not fail the request.

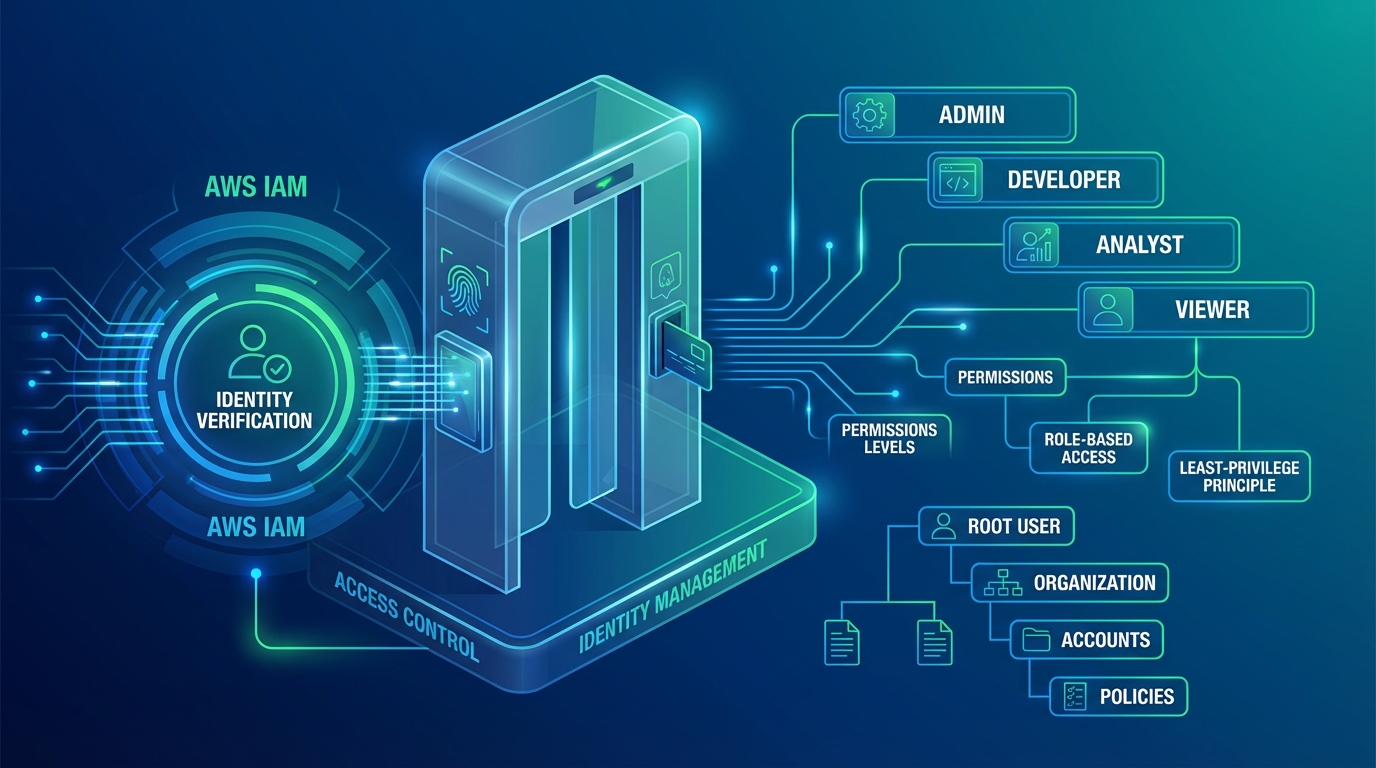
AWS IAM Identity Center is the AWS-native workforce SSO and identity-propagation service. This guide covers federation from Okta / Microsoft Entra ID, permission-set design, attribute-based access control (ABAC), identity propagation to Q Business / Redshift / QuickSight / S3 Access Grants, and the migration off long-lived IAM users.

Most AWS security breaches aren't caused by AWS failures — they're caused by misconfiguration. Here are 10 concrete best practices to harden your AWS environment in 2026.

Least privilege is a slogan. Working IAM at production scale is a different problem. Roles vs users, permission boundaries, SCPs, identity federation, and the access-control patterns that keep teams fast without leaving keys lying around.

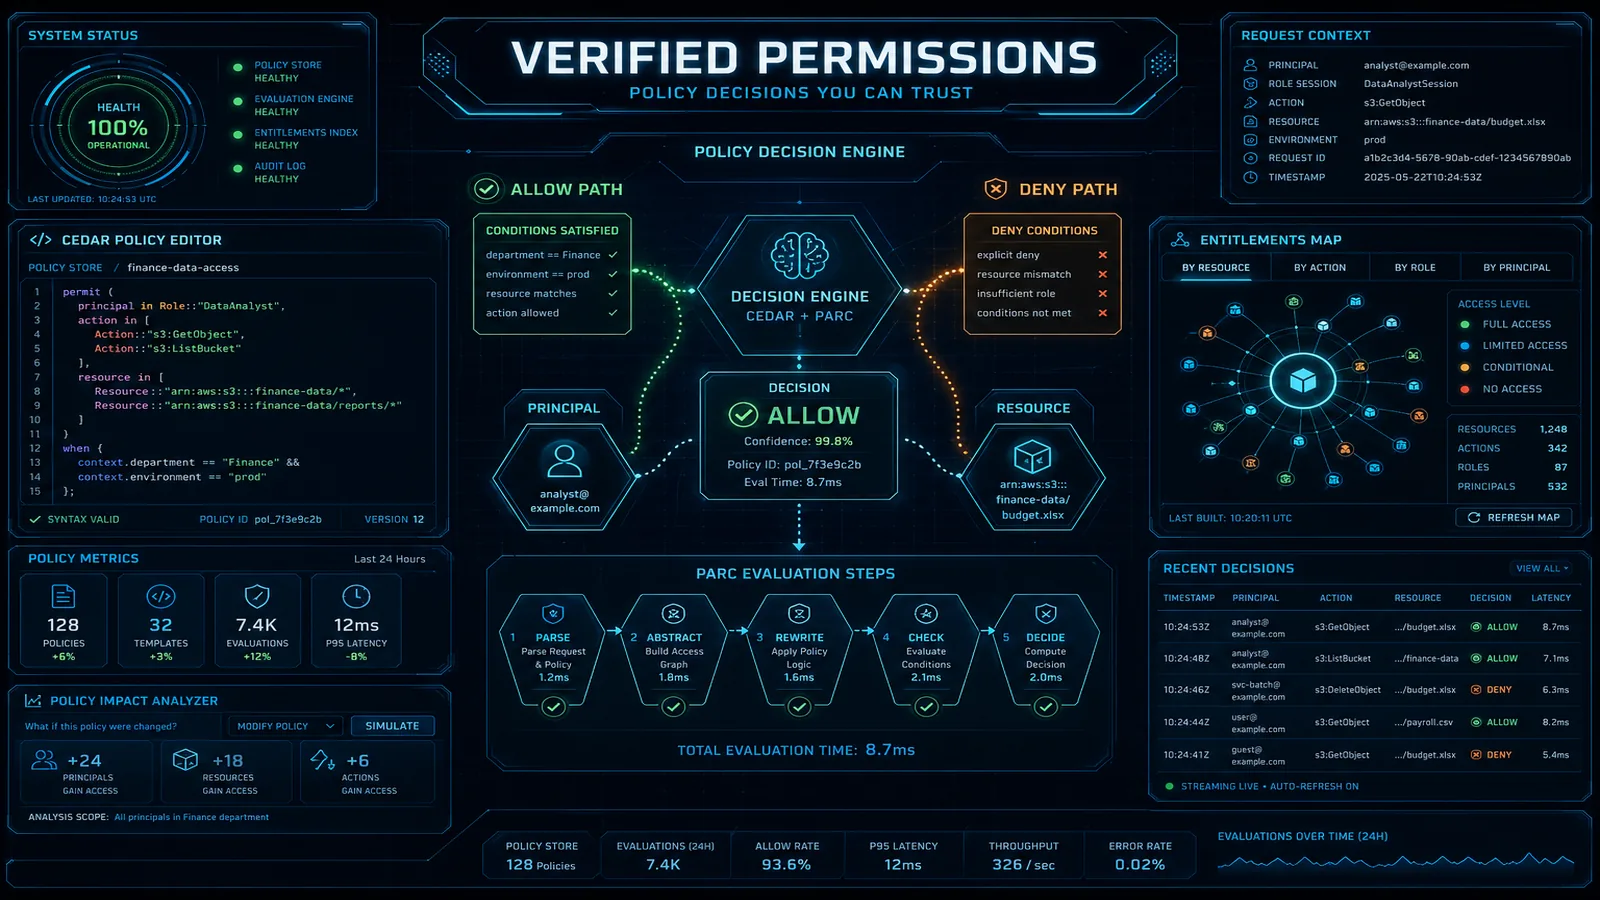
Amazon Verified Permissions externalizes application authorization logic using the Cedar policy language. Here's how to replace home-grown RBAC with a centralized, auditable policy store on AWS.

IAM best practices, GuardDuty, Security Hub, and the layered approach to AWS security consulting that keeps your workloads protected.